Luxury Island Getaway: Atmosphere Kanifushi

Shereen Shabnam

Escaping to a secluded Island to escape the pandemic is on the mind of many and we recently discovered the perfect luxury retreat at Atmosphere Kanifushi where private island laid back life meets award winning mouth-watering culinary adventures and spa indulgence.

We arrived at the pristine Kanifushi resort after an exhilarating 35-minute seaplane ride from Malé. welcomed by musicians on the island that is blanketed by dense tropical vegetation and blessed with vibrant, natural coral reefs.

Situated amidst the azure ocean with stand-alone beach and water villas spread along the 2 kilometres long island, we enjoyed impeccable service and elegant living spaces with picture-perfect surrounding ocean and serene sunsets.

At Atmosphere Kanifushi, the convergence of cotton candy clouds in the day, fiery orange skies in the evenings and turquoise waters during boat rides imbed an image that will be forever seared in our memories.

The five-star resort offers an all-inclusive luxury package, an extensive range of restaurants and bars plus a choice of excursions, sunset fishing, snorkelling and discounts on spa treatments and diving. Atmosphere Kanifushi has some of the best diving in the Maldives. The resort is five-star luxury all the way.

Dining at the Atmosphere Kanifushi is a delight as the resort has Maldives first top-quality vegetarian restaurant and a great all-day restaurant offering sumptuous ‘all you can eat’ buffet-style selection of Asian, European, and Maldivian favourites, live cooking stations, theme nights, and grills. Guests can also enjoy Selection of snacks during the day and a la carte fine dining experiences.

Activities at Atmosphere Kanifushi include sunset fishing, boat excursions, water sports with Dive and Sail, complimentary snorkelling equipment for every guest during the stay, snorkelling excursions and much more. There is a fully equipped gym with flood lit tennis and a children’s centre.

The rooms at Atmosphere Kanifushi come with stunning views. The water villas stretch along the crystal-clear lagoon, perfect for a romantic getaway. The outdoor deck comes with comfortable sun loungers and features a wooden ladder leading to the marine life-rich lagoon for a dip in or a swim anytime.

The sunset beach villas offer a secluded sanctuary where one can soak in the pleasures of island living in a private garden complete with lush tropical shrubs, soft sand beneath your feet, and an inviting private pool. There are also over water villas with a pool offering ultimate overwater luxury. The rooms have a luxurious bathroom and world-class amenities designed to indulge all senses.

The Kanifushi Grand one-bedroom villas have sweeping oceanfront views with a fabulous poolside setup, an airy, luxurious bathroom with a deep alfresco bathtub for an indulgent experience.

The two-bedroom sunset family beach bungalows have two interconnected rooms with a combination of indoor and outdoor spaces making it the best private villa in Maldives. With easy access to the kid’s club, sports complex, and the main restaurant, these villas are perfect for experiencing all the activities that the resort offers.

The Kanifushi Residence is a dream family hideaway, complete with a living cum dining room with a pantry, an entertainment room with two bedrooms and an attached nanny’s bedroom. This sprawling residence with extra privacy is ideal for large families, groups who want to share a common space, and multi-generational travellers.

Atmosphere Kanifushi serenades you with white, sandy beaches, swaying palm trees, and lush tropical gardens. We definitely felt the staff were the resorts best asset at Atmosphere Kanifushi as they offer impeccable service for blissful relaxing experiences and by going that extra mile for guest comfort and convenience.

#AtmosphereKanifushi #Kanifushi #Maldives  #visitmaldives #Hotel #Holiday #Destination #Beach #Staycation #travel #Island #tropical #Getaway #globaltrendmonitor #magazine #mydubai #lifestyle

Turkish Mangal Meets South African Braai

Explore traditional BBQ experiences at Turkish Village Restaurant

One of the most socially interactive culinary experiences the world over is having a barbecue with friends and family and this concept is most popular in South Africa, where a ‘Braai’ or barbecue can be a weekly experience.

In Dubai, the best on table barbecue experience comes in the form of the Turkish Mangal at the award-winning Turkish Village Restaurant where chefs use premium meat, authentic Turkish ingredients and flavors and like the South African Braai, the meat is cooked over sizzling hot coals to bring out the best flavours in the meat.

The atmosphere surrounding a Turkish mangal experience and a Braai is one full of enjoyment and common on weekends, birthdays, national holidays, graduations and on any occasion to celebrate with family and friends.

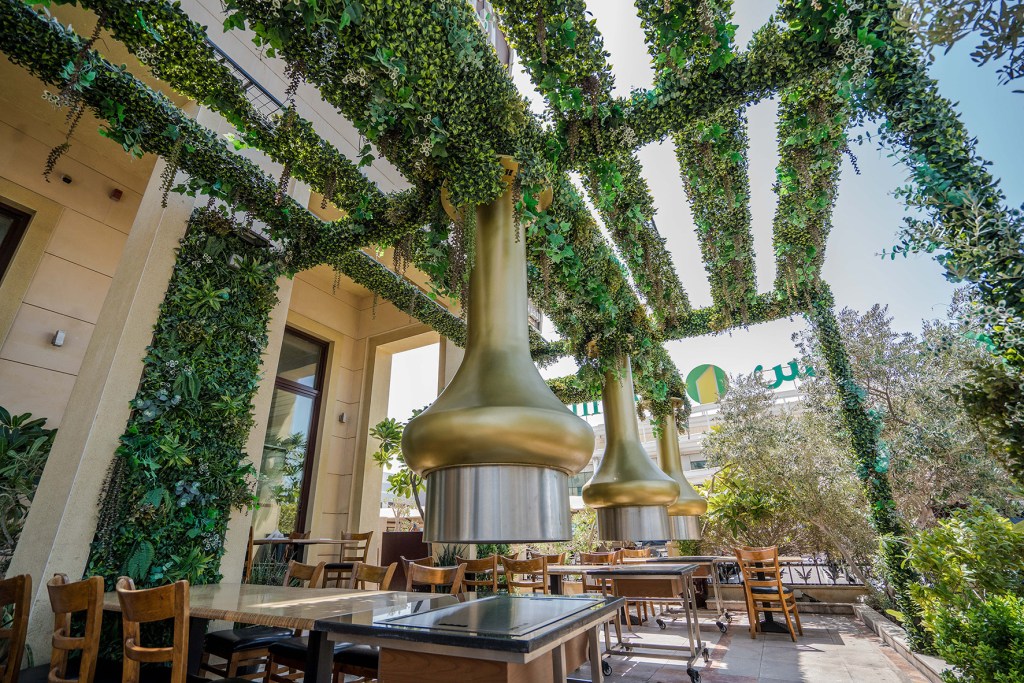
At Turkish Village Restaurant, diners select premium meat cuts and marinated meat from the restaurant’s in-house butcher to enjoy a feast at grill tables that come equipped with a private charcoal barbeque and a custom-made extractor. The choice of meat includes marinated chicken, kebabs, lamb chops, sausages and beef cubes for guests to prepare the meal together with friends and family.

The Mangal or Braai experience is ideal for gatherings during lunch and dinner at AED 50/- per person that includes charcoal, water, ayran, salads and cold starters on the table while the chicken and meat can be availed starting  at AED 110/- per kg to share. The meal is also served with fresh bread out of the oven, a selection of sauces and water or ayran.

Diners can end the meal on a sweet note with traditional Turkish sweets that include kunafa, milk infused tres-leche cakes, baklava stuffed with cream and pistachios as well as the creamiest baked rice pudding in the city.

The three level Turkish Village Restaurant is located strategically in Jumeirah 1 (across La Mer, next to Spinneys and the Jumeirah Grand Mosque), and in Dubai Festival City Mall promenade overlooking the fountains. It offers a laid-back memorable and interactive dining experience, within a warm and welcoming ambience. It is also a one-stop shop for artisanal Turkish products.

For bookings please call +97143449955 or send to reservations@turkishvillagedubai.com

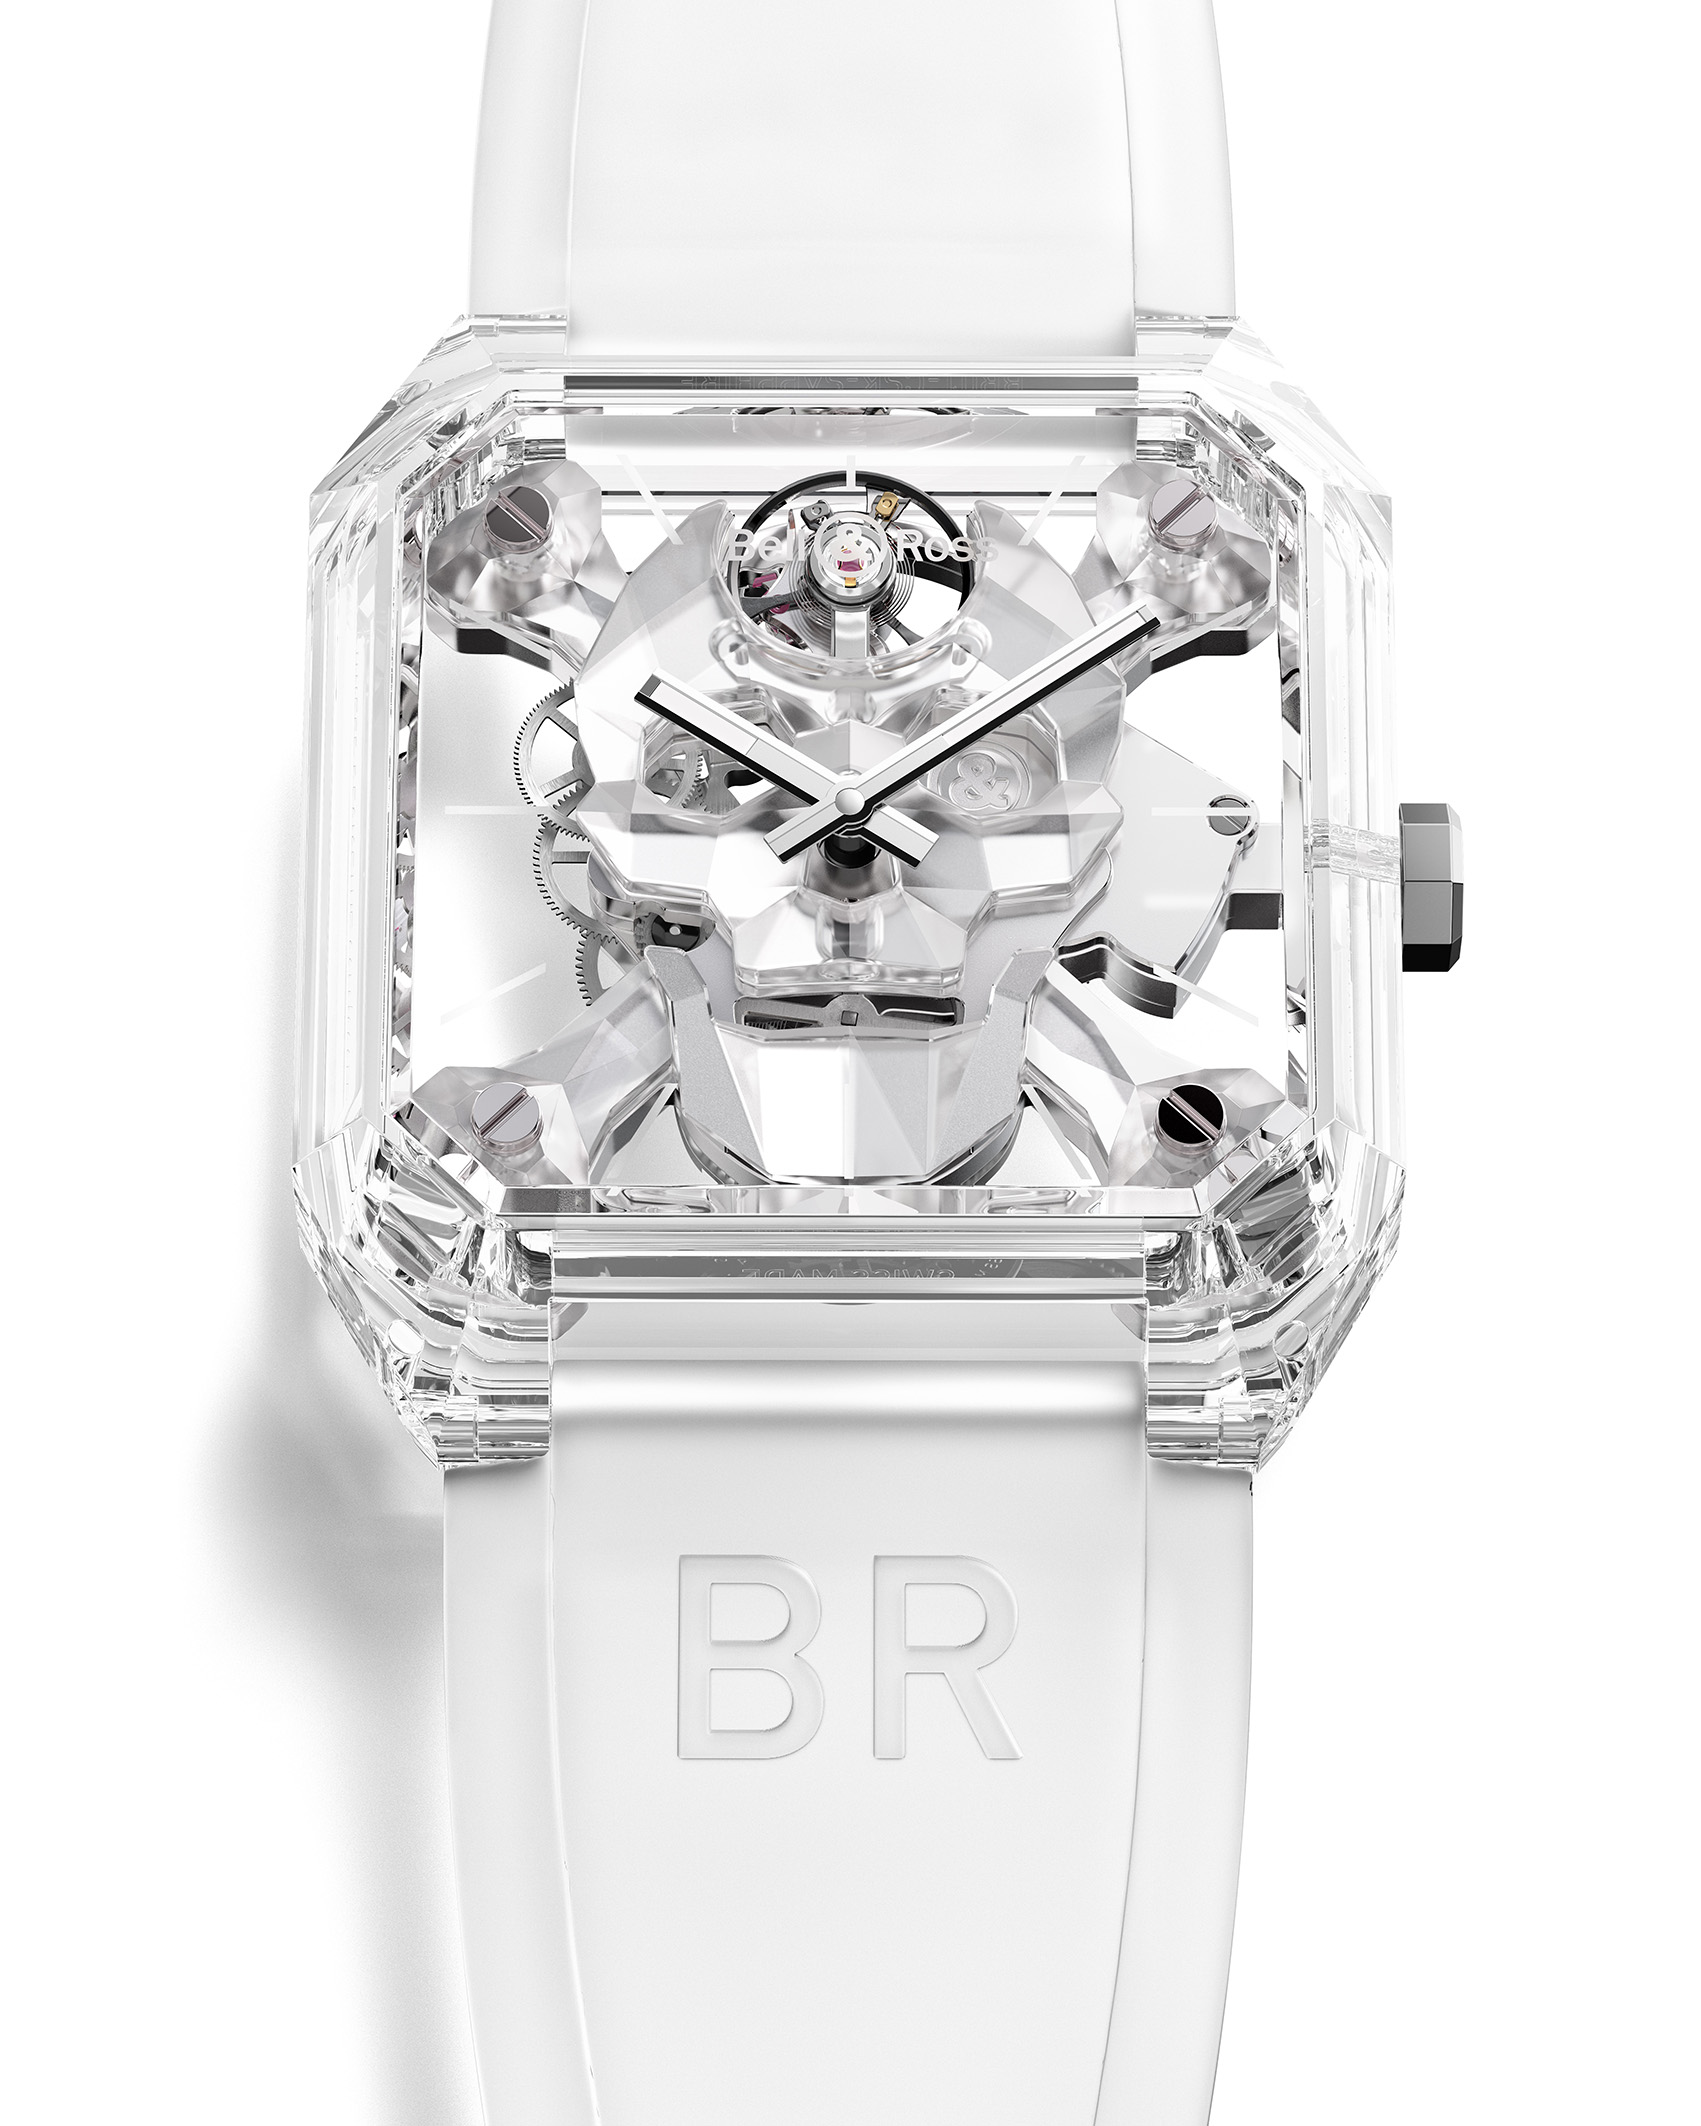
BR 01 CYBER SKULL SAPPHIRE

Bell & Ross sometimes  enjoys abandoning its usual themes of aviation and the military. In 2009, the watchmaker became one of the first to create a skull watch. Since then, the BR 01 Skull family has grown to include ten members which are greatly sought after by collectors.

In 2020, the avant-garde Cyber Skull revisited this iconic series.  Its faceted design represented a leap into the future.  And it was a resounding success.

The latest  Cyber Skull Sapphire  is a completely translucent, full sapphire  version. This technical material fires this icon of the watchmaking world into the realm of transparency and wealth.

NUMEROUS VERSIONS

In 2009,  Bell & Ross became one of the first watchmakers to create a skull watch.  The BR01 Skull includes  a skull and crossbones  in the company’s  iconic “circle in a square” case. It was an immediate success.

Bell & Ross then launched other versions.

– In 2016, the Burning Skull introduced  more volume to the skull surrounded  by flames. This provided the whole with a 3D aspect.

– In 2018, the Laughing Skull incorporated an automaton movement. The jaw moves when winding the crown so that the skull seems to be laughing. Spooky!

– 2020 saw a major break! The new Cyber Skull inaugurated a spectacular black ceramic case with truncated corners and a “pixelated” skull. This avant-garde  design fired this watch into the realm of ultra-modernity. It would go on to enjoy great success.

– In 2021, the Cyber Skull Sapphire  Only Watch  21 adorned the case with sapphire crystal. With its orange-coloured skull, this unique model was sold at the Only Watch  charity auction.  The hammer  finally fell at a price of 220,000 euros, twice its top estimated value. A genuine success!

– The latest Cyber Skull Sapphire  is the “general public” version of this exceptional watch. It reproduces the full sapphire case. However, the faceted skull is transparent on this version. It is a limited version of 10 items. Already a sure value for collectors.

NUMEROUS INSPIRATIONS

The design of this new Cyber Skull Sapphire  breaks  with the other skull watches  in the neo-vintage style. The sharp edges of the case play with the light, with the multiple facets  multiplying the perspectives and reflections.

It draws on several sources of inspiration:

– Avant-garde: it pays homage to the ultra-modern world of informatics and virtual technology. The faceted, pixelated design is a tip of the hat to the digital arts.

– Origami: its angular design is reminiscent of the ancestral

Japanese art of paper folding, transposed into the future.

– Military: the case is shaped like the fuselage of an American F117 stealth bomber. This faceted design allows it to vanish from radar screens. All eyes, however, are on the Cyber Skull Sapphire.

THE TRANSPARENCY   OF SAPPHIRE

The BR 01 Cyber  Skull Sapphire is a UFO of the  watchmaking world. The base is a Cyber Skull, which has nevertheless been developed entirely in colourless sapphire crystal. It plays the transparency card to the full, including in the translucent rubber strap.

The skull and crossbones are captured between two sapphire crystals, so that they appear to be floating in the air.

Initially, the sapphire is a precious block of very hard glass. A material  that is very difficult to shape.  The slightest  error means starting all over again.

THE MOVEMENT

The  BR 01 Cyber Skull Sapphire  combines design  and watchmaking  excellence. This high-end watch boasts a BR-CAL.209 automaton  movement. Specifically developed for the watch, this manual-wind skeleton calibre is almost invisible. It takes the form of the skull. The skeleton  form reveals some of the interesting technical parts, including the cogs, balance and more.

The plate and bridges follow the outline of the skull before extending below the crossbones. The spring balance placed at “twelve o’clock” symbolises the brain in this skull which is very much alive.

Are You Prepared for More OT Threats?

By Rick Peters, CISO Operational Technology, Fortinet

For years, Operational Technology (OT) systems have been working to control everything from factories to transportation networks to utilities. The reality is most citizens don’t think about these systems until there’s a problem. That’s why the the attack against Colonial Pipeline in May 2021 was so startling. The attack on a segment of the enterprise transcended IT and resulted in a temporary but severe disruption of the OT based fuel supplies and led the Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) to issue an advisory urging critical infrastructure (CI) asset owners and operators to take on a heightened state of awareness.

Unfortunately, the attack against Colonial Pipeline isn’t the first or last time an adversarial cyberattack on an OT target will make headlines. Malicious cyberattacks are likely to increase given the opportunities for mission impact, social anxiety, and profit that disrupting systems and stealing intellectual property from OT and IT systems represent. If there’s any silver lining to this high-profile attack it’s that it has put a renewed focus on securing critical OT assets.

OT cyber events also have demonstrated the consequence of failing to invest and commit proportionally to a cybersecurity strategy. For years OT system owners relied on the “air gap” that separated OT systems from IT to protect them. But as more and more OT organizations digitally connect OT infrastructure such as supervisory control and data acquisition (SCADA) systems with IT networks, the resulting evaporation of the air gap has dramatically increased the level of risk. Given this situation, it’s not a surprise that in the “2021 State of Operational Technology and Cybersecurity Report” 9 out of 10 OT organizations experienced at least one intrusion in the past year and 63% had three or more intrusions.

To protect cyber physical assets, OT organizations need to commit toa proactive cybersecurity strategy, paying particular attention to visibility, control, and behavior analysis. It’s critical to protect every point of connection to the outside world to proactively safeguard OT.

OT Is No Longer a Niche Exploit

In the past, exploits against SCADA or industrial control systems (ICS) were viewed as an infrequent subset of highly structured and often nation-state sponsored targeted attacks. But the OT market is expected to continue to grow through 2027 at a CAGR of 6.40%. Relying on obscurity as a defense strategy doesn’t work anymore; it’s practically an invitation to cybercriminals to penetrate and ultimately compromise OT systems. Although IT-related exploits are still more prevalent, according to the Global Threat Landscape Report from FortiGuard Labs, a growing number of  exploits are targeting OT. The long-held perception that ICS exploits are an obscure niche of the cyber threat landscape is simply no longer the case.

Why Now?

In the past, OT attacks were the domain of specialized threat actors who knew how to exploit ICS and SCADA systems. But now, many of those tools are now being packaged as attack kits on the dark web, so they are available to a much broader set of less technical attackers. The motivations behind the attacks range from gaining a profit through extortion, stealing intellectual property, to simply testing infrastructure resilience. The attacks offer a side benefit in that they create a climate of uncertainty and can force actions by executives in the government and commercial sector. The headlines generated from a successful attack on OT infrastructure only serve to amplify these effects. Attacks on large enterprise businesses in energy and manufacturing and even smaller more discrete intrusions at the municipal utilities level are all newsworthy. The alarming cybersecurity news in 2021 reinforces the fact that OT infrastructures require attention to reduce the attack vectors, tactics, and techniques that focus on industrial environments.

The Need for Better Visibility

The rapid expansion in the threat landscape and the increase in attacks demonstrate the increased need for integration between enterprise solutions and operational infrastructure. In most cases, security considerations need to extend to on-premise systems and extend to the Internet of Things (IoT) and Industrial Internet of Things (IIoT) devices. It’s also important to have an infrastructure control strategy that restricts and contains suspicious activity and behavior. At a minimum, organizations should implement zero-trust network access (ZTNA), which limits user or device access to only those resources required to perform a specific role or function. ZTNA also strictly limits the range and level of engagement, which serves to restrict activity if a system is compromised. 

OT organizations that put comprehensive security policies in place give themselves an advantage over threat actors and can limit the impact of a breach. OT infrastructure is no longer benefiting from obscurity and the adoption of near-universal convergence of IT and OT networks implies traditionally isolated environments are no longer safe. Organizations must take proactive steps to harden OT environments, including integrating tools and practices designed to protect, detect, and respond to threats in real-time. Although attacks are inevitable, they don’t have to be successful.

Help AG Named Platinum Partner by Trend Micro

The partnership will enable Help AG customers to avail of Trend Micro’s security capabilities without sending their data to the cloud, alleviating concerns regarding data privacy.

Help AG, the cybersecurity arm of Etisalat Digital, today announced its Platinum Level partnership with Trend Micro, a global leader in enterprise data security and cybersecurity solutions. The partnership will enable Help AG customers in the United Arab Emirates and Saudi Arabia to avail of Trend Micro’s security capabilities without sending their data to the cloud, alleviating concerns regarding data privacy.

This collaboration allows Help AG to service clients that may be reluctant to transfer sensitive endpoint data to the cloud environments of cybersecurity providers. When utilizing Endpoint Detection and Response services, the client needs to provide complete and accurate endpoint data in order for the service provider to be able to detect threats and attacks. This can be problematic if an organization’s users engage in confidential activities or access confidential websites.

Help AG’s partnership with Trend Micro addresses these challenges by delivering security services and capabilities without needing clients to send their data to a cloud-based environment. Due to the unique data model it has in place, Trend Micro is one of the few vendors of its calibre to offer this option, answering the needs of a niche segment of customers with specific data privacy concerns.

Commenting on the partnership, Stephan Berner, Chief Executive Officer at Help AG, said: “Trend Micro offers solutions that cater to our customers who are sensitive about utilizing cloud for some or all of their security services. Joining forces with Trend Micro enables us to address their concerns by delivering robust capabilities in an environment that is suitable for their data privacy preferences and needs.”

Berner added: “It is an honor to be named a Platinum Partner of Trend Micro, a highly respected leader in the cybersecurity space with a long history and rich legacy. Trend Micro has been extremely consistent in providing world-class products and solutions that address the security needs of organizations, and our customers will benefit immensely from having access to their portfolio.”

“Our partners are at the heart of our mission to make this world a secured place for exchanging information digitally,” said Dr. Moataz Bin Ali, Vice President and Managing Director, Middle East and North Africa for Trend Micro. “We are excited about our collaboration with Help AG that will empower its customers with robust security capabilities to protect their data, adhering to their privacy and compliance needs. Together, we will help regional organizations reimagine cybersecurity,” he added.

Now available to Help AG customers, the Trend Micro portfolio includes products and solutions related to Detection and Response, Network Security, User Protection, Cloud Security, Internet of Things Security, Enterprise Ransomware Protection, and Regulatory Compliance, among other areas within cybersecurity that are relevant to organizations today.

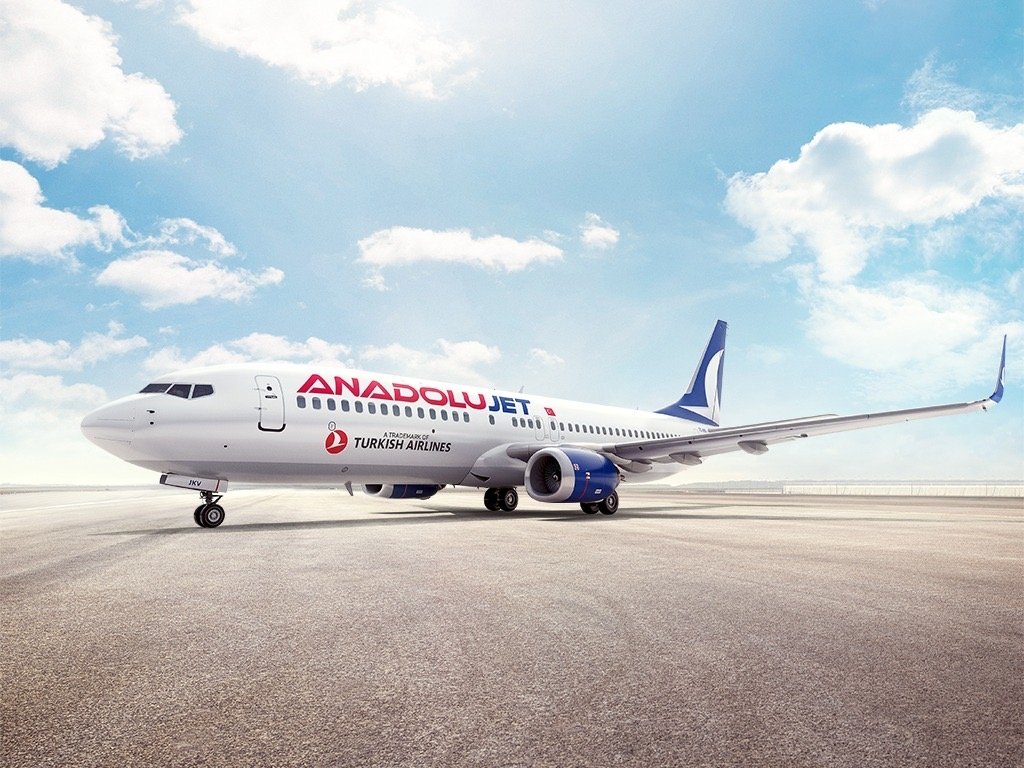
AnadoluJet is starting its Sharjah – Istanbul flights

AnadoluJet, the brand of Turkish Airlines, is starting Sharjah – Istanbul flights. For the launch, the flag carrier brand will set the prices of tickets starting at 755 AED for round trips from Sharjah.

Starting on 15 December 2021, AnadoluJet will operate reciprocal flights four days (Monday, Tuesday, Wednesday and Sunday) a week between Sharjah and Istanbul Sabiha Gökçen. Flights will depart from Sharjah International Airport, flights will depart at 01:20, from Istanbul Sabiha Gökçen Airport at 20:15 on Mondays, Wednesdays, Sundays and at 20:20 on Tuesdays in local time.

AnadoluJet guests will have the option of making changes to their tickets until (including) 31 May 2022 if purchased before (including) 31 March 2022. For more information, you can visit http://www.anadolujet.com website and learn about the details of your options on cancellation, refunds and changes on the “Flexible Ticket Rights” page.

AnadoluJet ensures that all hygiene precautions are always taken at the highest standards in order to provide a healthy and safe travel experience for its passengers and flight crew. For detailed information, you can visit our website at www.anadolujet.com/en/corporate/news-and-annoucements/guidelines-for-safe-travel.

Invixium Integrates Biometric Solutions with AEOS by Nedap

Invixium Integrates Touchless Face Recognition and Multi-Factor Biometric Solutions with AEOS Access Control

Invixium, a premier manufacturer of innovative touchless biometrics, has integrated its portfolio of modern solutions with AEOS by Nedap, a leading provider of access control solutions. This integration between AEOS and IXM WEB, Invixium’s enterprise-grade software solution, streamlines the process of setting up and using Invixium biometric systems with AEOS. AEOS users can now seamlessly deploy Invixium touchless biometrics, such as face recognition via IXM TITAN, as well as the rest of Invixium’s world-class biometric portfolio.

This integration is powered by IXM Link, a licensed software feature for IXM WEB that allows for one- or two-way database-to-database synchronization between IXM WEB and AEOS. Database synchronization ensures easy setup, installation, and use of Invixium biometric solutions for AEOS users. Administrators can effortlessly enroll biometric data to cardholders (securely stored in IXM WEB) which are continuously synchronized with AEOS. In addition, Device Integration Protocol (DIP) has been implemented to allow AEOS to control the verification process.

“Integrating leading security solutions, such as touchless face recognition, with AEOS has enabled Nedap to remain at the forefront of COVID-19 response,” said Susanne Adriaanse, Managing Director at Nedap Security Management. “Invixium’s innovative technologies like face recognition, mask detection, and touchless thermal screening make them a partner that closely aligns with our strategy to provide a wide range high-level solutions to modern security problems.”

“Expanding our reach through technology integrations is vital to our strategy,” said Shiraz Kapadia, CEO & President at Invixium. “This integration simplifies installation and management while reducing costs for businesses that are looking for unified end-to-end security systems. We look forward to addressing the needs of AEOS users with our unique solutions.”

A Cybersecurity Diagnosis for the Healthcare Sector with Breach-Likelihood

By: Saket Modi, Co-Founder and CEO at Safe Security

For more than the past decade, healthcare has been the biggest target of data breaches. The total average cost has increased to $9.23 million in 2021 from $7.13 million the previous year, demonstrating a 29.5% rise. Cyberattacks in healthcare are unfortunately not limited to their financial, regulatory, and reputational impact since they have a direct consequence on lives. An Alabama-based resident claimed negligent homicide for the death of her infant because the hospital’s fetal monitors were inaccessible as a result of a ransomware attack, leaving its systems locked for eight days. For instance, if a hacker tampers with CT or MRI scans, it could also lead to incorrect medical procedures/surgeries, incomplete diagnoses, and reduced emergency or urgent care.

In such a scenario, the healthcare sector needs to quickly improve its cyber risk management. This is possible only if they move away from the traditional reactive and point-in-time approach in cybersecurity to adopt a predictive and measurable method instead. Adopting a proactive strategy includes knowing the organization’s breach-likelihood in real-time and its financial impact on the organization.

The current state of cybersecurity in healthcare:

The NotPetya attack happened five years ago. Since then, has much changed in the healthcare sector? The cost of ransomware alone has grown by 1094% since 2015. However, there are three key areas where this sector falls short:

  1. Accidental and/or malicious insider threats: The HIMSS Cybersecurity survey 2020 states that 89% of initial compromise in hospitals is still through emails and more than half (57%) of the cyberattacks in healthcare begin via trusted insiders.
  2. Third-party are unsecured often with unrestricted access: Over 1600 insurers at an average share PHI with hospitals. Hospitals also deal with a large number of medical devices suppliers, vendors for equipment, medication, repairs, and more, each third party is likely to be an entry point.
  3. Medical device security: There will be ~50 billion medical devices by 2028, with 15 – 20 IoMT in each hospital room, creating a vast digital attack surface. Interestingly, while one aspect is digitizing faster than it can be secured, 83% of medical imaging devices are still legacy systems too old to receive software updates.
  4. The lack of a designated security team: 87% of healthcare IT security leaders work without the right personnel, and three in four hospitals are operating without a designated security leader.

Can predictive analytics in cybersecurity help the healthcare sector?

Financial services organizations predict the likelihood of loans being repaid using the financial history of the applicant, their previous loans, salary/income, and credit score. Similarly, OTT platforms use predictive analytics and algorithms to improve their suggestions. The medical fraternity too relies on prediction models to improve diagnostics, identify risk groups, and improve patient care. Why not use the same analytical approach to predict the possibility of a breach rather than detecting cyberattacks after they happen and reacting to them? The use of predictive technology and models such as the Bayesian Network to predict cyber breaches makes this possible.

Enterprise cyber risk is a product of the probability of a breach happening and its business consequence. This probability is termed the “breach-likelihood” of the organization and can be calculated at the most granular level. Starting from the breach-likelihood of each medical device in every room, department-wise employee threats, to vendors or suppliers of equipment and pharmaceuticals, Electronic Medical Records directory on the cloud and the security posture of each cloud asset – the possibilities are endless. Each prediction makes the organization that much more prepared to predict and therefore mitigate breaches. Once an organization knows what to expect, it can focus energies on fixing what really matters rather than carrying out ad-hoc activities which only add to a sense of security rather than real cybersecurity.

How does breach-likelihood help the healthcare sector?

Breach likelihood in the healthcare sector can be a gamechanger in giving the visibility that is missing today. Similar to doctors arriving at a diagnosis after carrying out due diligence, sieving noise from actual symptoms, and aggregating all relevant information to a central database, cyber risk quantification can segregate information from noise.

As healthcare organizations ramp up cybersecurity infrastructure, they need to remember that all cybersecurity services, products and processes implemented in their cyber risk ecosystem need to communicate with each other. In a scenario where tens of cybersecurity services and tools are performing well in silos, but together fail to generate a comprehensive and prioritized solution, breach-likelihood is can create one score to drive cybersecurity strategy.

Cybersecurity Leader Spearheads Service-Centric Evolution by Launching Help AG as a Service

Help AG, the cybersecurity arm of Etisalat Digital and the region’s trusted security advisor, has launched “Help AG as a Service,” a service-centric model that provides comprehensive cybersecurity offerings that customers can avail “as a service” based on state-of-the-art platforms and tools. This highlights Help AG’s position as a pioneer in the Middle East’s cybersecurity sector, spearheading the industry’s move towards a service-centric future.

Help AG as a Service is the culmination of the company’s transition from technology delivery to a service-centric model, which has placed it in the best position to offer the entire lifecycle, from ‘Assess’ to ‘Defend’ to ‘Respond,’ as a service to customers.

With Help AG as a Service, customers can rest assured that they are provided best-of-breed services, irrespective of the underlying technology or deployment model. Driven by its vision to offer the highest level of protection and user experience, Help AG delivers future-ready services in terms of people, processes and technology, on an MRC/PAYG model.

All services delivered by Help AG are fully compliant with regional and country specific data regulations, and the company ensures that it has expertise and infrastructure available on the ground. Help AG follows the concept of ‘think global, act local,’ aiming to give customers all the benefits of the most advanced global technologies, while fully provisioning them with local expertise.

Commenting on the launch, Stephan Berner, Chief Executive Officer at Help AG, said: “Help AG has been one of the region’s most experienced and trusted cybersecurity partners for more than 16 years, and with the launch of Help AG as a Service, we are truly cementing our place as a pioneer in the regional cybersecurity industry. The future of cybersecurity will be service-led, and Help AG is at the helm of this evolution.”

Berner added: “Years ago, we built our service offering from the ground up with a commitment to delivering truly global and advanced security services while moulding them to address regional market threats and requirements. Our offering has been received very well in the market, enabling us to become the biggest Managed Security Service Provider in the Middle East, and driving us to take our service-centric transition to the next phase with Help AG as a Service.” 

Under Help AG as a Service, customers also enjoy SLA-based offerings; cybersecurity expertise on demand, wherein Help AG’s experts work as an extension of the customer’s team; and elastic capacity based on the customer’s needs.

Help AG has already standardized many of its services, including 24/7 Threat Monitoring, Detection and Response, and it has applied automation to several existing services, including its Managed Advanced Web Application Firewall (AWAF) service and Secure Access Service Edge (SASE) offerings, namely Cyber Edge X and the Help AG Secure Private Access Service (HPA). Other best-of-breed services offered by Help AG include Penetration Testing, Red Teaming, Security Awareness, Compromise Assessment, Managed Security Controls, Digital Risk Protection, SMB Security Offerings, Always-On DDoS Mitigation, Security Bundles with Service Providers, and Secure Cloud Offerings.

Help AG continues to invest in developing its capabilities to provide a 360-degree portfolio of cybersecurity services to customers with round-the-clock availability. The company has differentiated itself by providing in-country, compliant security infrastructure; capability and agility in the cloud; optimization-driven service delivery; in-house digital forensics and incident response; automated threat hunting and cyber threat intelligence under its Security Operations Center (SOC) services; and a dedicated team of security researchers with 110+ zero-day findings to its credit, among other factors that add unmatched value for end customers.

Help AG as a Service is built on the foundation of the capabilities the company has cultivated over more than 16 years, delivering the highest quality of services at the best possible prices. With its integration into Etisalat, Help AG now offers secure connectivity coupled with unmatched availability and reliability through state-of-the-art, in-country infrastructure, thereby complying with customers’ data residency needs. The ongoing transition to a service-based model across the cybersecurity industry is increasing the importance of the role of Managed Security Service Providers (MSSPs), and with Help AG, enterprises get access to the best and largest MSS team in the region, as well as a flexible financing model, hence investing in a capability that will evolve over time.

NetApp 2022 EMEA Predictions

By Fadi Kanafani, Managing Director – Middle East at NetApp

  1. “Digital first” as new business paradigm
    While IT teams and IT leaders are historically called on to drive digitization and increase value, the roles will be reversed in the post-pandemic world. Strategic decision making starts with digital experience and digital transformation since they are now deeply connected to the successful operation of any company.
    We see this for example in business analytics, where the analysis of user experience journeys or customer experience journeys become a crucial information source for strategic decisions.

Another example is increasing convergence between the online and offline world, which results in digital twin concepts being adopted beyond production, and any process being tested virtually before being considered for rollout.

  • Cyber security and resiliency
    The pandemic months have triggered a rapid increase in ransomware attacks as more and more people worked remotely. Coincidentally, this opened up a multitude of new infection vectors.


Enterprises had to come to terms with the fact that many IT security processes and protocols are not well suited to the fight against ransomware, because it is virtually impossible to cut off all these infection routes, especially when criminals use social engineering.


Instead, enterprises will rely on AI-based prevention across their whole domain and stringent zero trust policies. Rather than preventing IT attacks from happening, this approach minimizes their impact. Once an infection happens, it is discovered almost instantaneously: Infected areas are cordoned off and infected files replaced in almost real-time.

  • Sustained impact of the pandemic: cloud acceleration and the supply chain
    The global supply chain has been brought close to its braking point by the COVID-19 pandemic and its impact on air, sea, and land travel. We predict that cloud adoption will accelerate faster as the supply chain constraints drive buyers to find alternatives to purchasing traditional on-premise infrastructure to meet demands. At the same time, optimization of production lines and business processes can help the system to become more robust in the future. Marrying IT and Operational Technology (OT), for example through digital twin concepts and technology such as IIoT and analytics, has virtually limitless potential. Companies that have done their homework in the past, e.g. by building out flexible Industry 4.0 production facilities, will be able to stay healthy much more easily.


The workforce is going through a major change cycle, also triggered and sustained by the pandemic. Hybrid working environments are the expectation of employees moving forward. The ability to work anywhere will increase the digital capabilities businesses must provide to their staff. Controversially, the pandemic also shone the light on labor shortages surfacing quickly and unexpectedly. This will be both a challenge and opportunity for high-skill sectors like the IT industry. On the one hand, there is bound to be fierce competition for skilled personnel; on the other hand, IT itself can deliver technologies that remedy the labor gap, such as low code, no code and AI software development.


The constant simplification of public services access and the services in general will drive broad buy in for digitization. People are also going to be more comfortable with providing their data because they have experienced the positive impact of virtualized service delivery.

  • Productized AI
    In 2022, artificial intelligence (AI) starts to permeate all industries. We will see it used in agriculture, food production, fast-food chains and the entertainment and hospitality sector. Agriculture and the food industry, for example, will use it for packing and processing, while other sectors gain most from general automation and the simplification of their processes.


Let’s also talk about the “how.” Managed services become a primary delivery mode for AI as CSPs double down on “GPU as a service”’-type offerings. This is an important facilitator: As more industries use AI to stay competitive and innovate, there needs to be a solid technology foundation that can scale accordingly, and AI users need to move their AI projects from standalone (siloed) infrastructure onto shared, virtualized, production environments.


Another driver is “Tiny Machine Learning.” Experts are forecasting a massive increase in AI at the edge, down to very low cost, extremely resource constrained edge devices. Think sensors rather than compute devices. This is another generation of devices that feed the ever-growing edge-core-cloud data pipeline, which industries need to access and leverage to differentiate themselves.


And, finally, the macro perspective on AI and machine learning becomes clearer. Countries and governments are guaranteed to invest in AI and ML capabilities to accelerate economic transformation and compete on a global basis.

  • Data trends
    There are a number of technology sub-trends that drive change and innovation. One is Analytics & Optimization of digital services. E.g., Finops results are much easier to come by as more automation and smarter applications take hold. This results in increases ROI from cloud investments throughout the public and private sector.
    Another trend concerns production environments. There is a clear move away from applications as companies deliver their services through containerized solutions and microservices.


Thirdly, data sharing regimes are important prerequisite for building a workable data economy on the international stage. GAIA-X sparked an important discussion about digital sovereignty and the contributions needed to establish a secure data exchange infrastructure. In the near-term, I don’t think this results in a sovereign “EU Cloud.” However, we will see more unity about European norms, and more adherence to them from outside Europe.


Lastly, specifically in data storage, NAS and SAN continue to be the technologies of choice to underpin digital innovation. Writeable storge media can still be made more efficient.

  • Quantum computing
    Quantum computing is expected to re-accelerate the performance cycle postulated by Moore’s law, and all major IT players are invested. Early use cases are expected to be delivered as a service but will not come into fruition for some time. However, manufacturers in different branches of IT will be more vocal about their quantum computing strategy in 2022 – for example security providers, hyperscalers, storage companies, and GSIs/global advisors. These manufacturers will also theorize how they can deliver quantum computing innovation as a service for their customers and overcome branch-specific limitations, e.g. building a data pipeline into the quantum computing cloud.
  • Sustainability – ESG becomes a competitive advantage
    Green topics are on the rise, as demonstrated by the 2021 Climate Change Conference, the US infrastructure deal, or the traffic light coalition coming to power in Germany. We predict that businesses will head in the same direction. This is partly due to regulatory pressure, for example to lower carbon dioxide emissions. But enterprises will also become intrinsically motivated to deliver green innovation.
    One are to look at is employee experience hybrid models, which basically allow companies to recruit talent everywhere, reduce office footprint, and significantly cut work travel.


Another area concerns production processes, which can be made more environmentally-friendly with the help of IT. More automation and optimization, flexible production, testing and planning in software, are all things that reduce wastage.


Net Zero targets will become a priority for businesses in 2022, and they are impacting corporate decision-making already now. This will result in companies examining not just their own actions but their supply chain, digital and non-digital, as they strive to deliver net zero (carbon emissions) as quickly as possible.