Help AG Advances AI-powered Cybersecurity Abilities with Exabeam Partnership

Further augmenting its capabilities in artificial intelligence (AI) and machine learning (ML) for cybersecurity, Help AGtoday announced a new partnership with Exabeam, the Smarter SIEM™ company. As the Middle East focus partner for Exabeam, Help AG will bring to market Exabeam’s industry-leading security information and event management (SIEM) and user and entity behaviour analytics (UEBA) solutions. This will empower regional enterprises to detect, investigate and respond to cyberattacks more efficiently and effectively.

This new partnership is in line with Help AG’s AI strategy. Over the last year, the security services and solutions provider has worked closely with several industry-leading technology vendors to develop and deliver practical and impactful use-cases for AI in the context of cybersecurity. 

Explaining how Exabeam furthers this strategy, Stephan Berner, CEO at Help AG said, “Through the application of AI to critical labour-intensive tasks, Exabeam expertly enables cybersecurity teams to refocus their efforts on risk rather than events. This is especially beneficial in the region, as these solutions can alleviate the workload on understaffed IT teams, while delivering an elevated ability to detect and mitigate the impact of complex cyberattacks.”

Exabeam is a recognised leader in the SIEM and UEBA marketplace. It offers the comprehensive  Exabeam Security Management Platform (SMP) that enables organizations to take advantage of big data, advanced analytics, and automation capabilities toreduce time to investigate and contain threats by 51 percent. Exabeam’s solutions integrate seamlessly with key technologies in Help AG’s portfolio – such as security solutions from Splunk and Vectra – as well as with cloud environments such as Microsoft Office 365, AWS, Google, and Salesforce. These integrations allow Help AG to unlock the full potential of our customers’ existing cybersecurity investments.

“Exabeam’s solutions perfectly complement the security technologies that form the core of Help AG’s product portfolio, thereby enabling us to create highly effective turn-key solutions for our customers. Furthermore, we have deployed these solutions within our own Cybersecurity Operations Centre (CSOC), thereby enhancing our 24×7 Managed Security Services (MSS) offering,” Berner said.

“As a truly advanced provider of cybersecurity services in the Middle East, Help AG is an ideal partner for Exabeam,” said Brett Candon, VP, EMEA Channels, Exabeam. “Together, we can help more enterprises investigate and respond to security events in minutes, not days, and enable security operations center analysts to work smarter. They are a welcome addition to our Exabeam Partner Program.”

Ensuring Cybersecurity at Big Events this Summer

By Alain Penel, Regional Vice President – Middle East, Fortinet

Does the arrival of summertime remind you of warm sunny days, the sizzle of the grill, trips to the beach, or the electricity of the crowd at the ballpark at the bottom of the ninth, bases loaded, as the home team’s star hitter steps up to bat?

Summertime living might be easy, but if relaxation brings a lack of vigilance, it can have devastating consequences for potential cybercrime victims. And the warmer months do come with some unique security risks, especially for IT teams working at stadiums and major event venues.

Summer is prime season for outdoor concerts, music festivals, and sporting events, when people tend to gather, both physically and online. And as a recent Fortinet Threat Landscape Report shows, attacks are increasing, cybercriminals are wily and shrewd, and are willing to take advantage of opportunities—both technical and human—wherever they can find them.

During the season when people gather, it’s essential for IT teams to be on guard against cyber attackers targeting crowds – especially on stadium and venue networks. If an event has brought thousands or even tens of thousands, of people together, it’s all too likely that most of those people are also using a mobile device connected to your wireless access points, and as a result, someone there will also be looking for ways to exploit your wireless network to target attendees.

Olympic Destroyer Sets the Precedent

Cyberattacks targeting stadiums, arenas, or event sites are nothing new. Cybercriminals are willing to target any element of a venue’s potential attack surface in order to compromise internal systems as well as the devices of paying customers. As we noted in last year’s Q1 Threat Landscape Report, an attack made headlines around the world when it disrupted the opening ceremonies of the 2018 Winter Olympics in South Korea.

Though the majority of cybercriminals are motivated by the desire for financial gain, high-profile events like the Olympic Games also make attractive targets for politically motivated threat actors, or for those seeking to alter the competition’s outcome by tampering with scoring equipment or monitoring systems. If they manage to cause damage, millions of eyes will be watching them do it.

With this in mind, IT and security teams at venues need to be aware of what poses the greatest risk to their own and customer security, and how to minimize that risk while meeting user demands and increased traffic.

Fans are the Biggest Target

At any major event, the fans connecting to your network are the cybercriminal’s most likely prey. In the excitement leading up to the big day, people attending a game or concert may be more likely to click on fraudulent websites or phishing emails related to the event. Attackers are also using a number of ticket generation sites to sell fake tickets before events even start. Once there, attendees may also fall victim to credit card skimmers or keyloggers at stadium ATMs. IT staff should be coordinating with the ATM providers to ensure these devices are secure and have not been tampered with.

It is also possible that attackers could target critical stadium infrastructure, like lighting systems or power supplies. However, a cybercriminal’s most probable target—because it can allow them access to the treasure trove of financial data stored on users’ mobile phones—is the event site’s Wi-Fi network. Nearly every large-capacity stadium, major league ballpark, or noteworthy concert venue today offers free Wi-Fi connectivity to the public. Younger fans, in particular, have come to expect faster and more reliable access to data than 3G/4G cellular networks can provide.

Unfortunately, many wireless networks, especially if improperly segmented and secured, are vulnerable to malware injection or man-in-the-middle attacks. Given the sheer size of many crowds, man-in-the-middle attacks can be especially difficult to detect. To reduce risk, venue IT teams must be up on the latest threat intelligence concerning Wi-Fi and router attacks, as well as the tools that are able to identify and pinpoint rogue access points so steps can be taken to remove them.

Wireless Networks Are Common Cyber Targets

Wireless routers are common targets for exploit. With this is mind, the challenge in securing these large events comes down to venue IT teams enforcing appropriate logical segmentation and segregation in its wireless network architecture.

Monitoring the huge spike in traffic that sporting events or concert attendees generate for a relatively brief period of time is a major challenge. It’s critical that IT teams maintain strong network segmentation during the event’s traffic spike, as well as ensure the physical security of the wireless access points and the ports they’re connected to. They also need to continually monitor for the presence of “evil twin” wireless networks set up in or near their facility to ensure attendees connect to the actual stadium network, and not a spoofed imitation set up by criminals to harvest their data or credentials.

Take a Look at the Security of Your Streaming Services

Even though the focus of this article is on protecting your physical venue, today’s marketplace, driven by digital transformation, requires that security be extended to online services. Many organizations are supplementing their revenue by offering streaming services. As a result, a number of cybercriminals are offering free lifetime passes to popular streaming services. These hacked accounts are available on the dark web, often for around $10 USD, and can take a serious bite out of not only streaming services revenue, but ticket sales, as individuals may be less willing to pay for tickets to an event that they can stream for virtually free.

You should also regularly check application stores and search for online sites to ensure that hacked or unauthorized versions of your application aren’t being offered, and coordinate with law enforcement to shut down free services being offered on illegal commerce sites on the Dark Web.

Taking an Integrated Approach to Event Cybersecurity

An integrated, end-to-end approach can help protect event sites and fans against cyber threats.

The key element in securing large-scale network architectures and infrastructures that need to handle tens of thousands of data connections on a temporary basis is appropriate logical segmentation. Traffic containing payment information (used for food orders, merchandise kiosks, or ticketing) should be isolated from internal traffic (facility maintenance IT systems, for instance), which should, in turn, be isolated from team and player communication traffic. Likewise, the wireless Internet access provided to fans should restrict them from communicating directly with each other, and should include filters and firewall policies to prevent user-on-user attacks.

Ultimately, the most successful approaches to this significant security challenge are those that rely on a comprehensive Security Fabric approach. Combining internal segmentation firewalls (ISFWs) with integrated security tools and sensors deployed across the environment, a proactively designed security fabric can detect and filter out attack traffic and prevent criminals from exploiting mobile application vulnerabilities. Additionally, secure wireless equipment can recognize spoofed wireless networks, and automatically alert the SOC to take action.

Securing major event venues as thousands of mobile devices attempt to connect to the network is a daunting task. By staying up to date on common WI-FI attack vectors and threat intelligence, event IT teams can implement the necessary controls and strategies to thwart cyberattacks, allowing everyone to just go back to enjoying their summer.

Data-Driven Bosch Jointly DevelopsInnovative Security Solution with NetApp

Bosch meets a higher level of security in video surveillance with NetApp data solutions.

NetApp (NASDAQ: NTAP), the data authority for hybrid cloud, and Bosch Building Technologies, the expert for security, safety and communication solutions, haveannounced the details of their joint high-performance security solution. The Bosch Video Management System (BVMS) is using real-time data, AI and IoT power to build a safer, more secure world. This is achieved by integrating NetApp Hybrid Flash Arrayswith the Bosch Video Recording Manager (VRM) for a revolutionary concept of storage virtualization. The NetApp operating system is writing different data streams directly from the camera to the storage in a compact format and with high storage density.The result: video streams and storage capacity are ideally balanced and arebacked-up in such a way that the processes continue to run even if there is a hard disk failure. Moreover, the system allows for highest scalability.

Advantages of the data-driven partnership

Data andits availability are critical to Bosch Building Technologiesand its customers. Among other solutions, its extensive product portfolio includes solutions for video surveillance, intrusion detection, access control, fire detection and evacuation systems, that help empower their customers to build a safer, more secure world. To be able to reliably map and record events as well as objects, a security solution needs industry leading resolution, refresh rates, dynamics, and light sensitivity. However, data must also be manageable efficiently. This is why Bosch Building Technologieshas been working with NetApp since 2011.

“We work with NetApp because they are the data authority”, said Bernhard Schuster, executive vice president sales and marketing at Building Technologies. “NetApp offers the technologies that ensure that our systems are up and running and makes managing large data volumes easy with maximum reliability while lowering costs.”

However, the digital vision of the Bosch team goes beyond security. For use at airports, company premises, hotel complexes and stadiums, recording alone does not do the job.

“Our video systems process image data in real time,” said Schuster. “Sharing the information with your security and other enterprise systems, such as warehouse or manufacturing is key for improving security and reducing costs.”

Greater security and efficiency can be achieved by a seamless transfer of data to higher-level systems. By adding IoT and AI, intelligent functions from sensor to connectivity turn the camera into an even smarter device that delivers valuable information in a digital infrastructure. Additional to the forensic capabilities of the system, suspicious activities are detected in real time by the device’s algorithm. This can include the detection of inventory theft, tracking missing shipments in large warehouses, or flame and smoke detection in seconds. That in turn enables the security operators to act quickly and efficiently.

High standards: security and efficiency in video surveillance

What is special about the joint solution is the unique integration of Bosch Video Recording Manager (VRM) and NetApp E-Series Hybrid Flash Arrays as part of BVMS. The NetApp operating system is writing the data stream directly to the storage. By means of virtualization, all disks can be managed by the solution as one large storage pool. Like this, the VRM can automatically balance video streams and storage capacity ideally, and back it up in such a way that the processes continue to run even in the event of a hard disk failure. The solution includes the following features:

  • Robust technology in a compact format and high-storage density on 12TB disks.
  • High integration for low complexity and maximum availability enables mapping of highly specific workloads.
  • High availability of data as two camera streams are recorded simultaneously in different recording qualities and sent to physically separated locations.
  • High scalability thanks to an entry-level range of complex environments with 200 cameras. There is virtually no limit to the number of cameras that can be mounted on top, as additional storage space can be added via BVMS.

“We are excited that NetApp technology is helping Bosch to achieve its data-driven vision of security”, said Alexander Wallner, senior vice president and general manager EMEA, NetApp.“By leveraging NetApp technology, Bosch Video Recording Manager solution is further enhanced, resulting in a high-performance, flexible, scalable and reliable storage management solution for IP network video recording.”

Bernhard Schusteradded: “With the help of NetApp and the power of data, we are pushing security to the next level.”

Spin the Wheel and Back To school sales back at Mushrif Mall

Shoppers to enjoy regular Spin the Wheel and back to school promotions

Back to shcool at Mushrif mall.jpg

Mushrif Mall in Abu Dhabi is set for the summer with its regular Spin the Wheel Fortune and upcoming back to school promotions.

Aravind Ravi Palode, Mall Manager of Mushrif Mall, said, “We have a host of retailers catering to children and the outlets will be curating a memorable shopping experience via special offers and discounts on school items for all age groups.”

Retailers popular at the Mushrif Mall during the beginning of the school season include LULU Hypermarket, PAPERCHASE, AROUND THE WORLD JASHANMAL, MY BOOK STORE, DAISO and HEMA.

Mushrif Mall, located on Airport Road, Abu Dhabi hosts renowned brands and a wide range of dining outlets, hypermarket and services spread over three levels. It has over 200 luxury fashion retailers across all categories including fashion, jewellery, electronics, home appliances, cosmetics, gift items, clothes, perfumes, toiletries and much more.

Alcatel-Lucent Enterprise partners with Aislelabs

Relationship set to enhance Wi-Fi offering

Alcatel-Lucent Enterprise (ALE), a leading provider of communications and infrastructure solutions, has signed a strategic technology partnership with Aislelabs, a provider of advanced cloud based Wi-Fi location marketing and analytics. The partnership will enhance the deployment of the ALE WLAN solutionby combining it with Aislelabs’ analytics platform to unlock the hidden potential of Wi-Fi infrastructure by turning WLAN into a powerful location and behavioral analysis tool.

The global demand for Wi-Fi marketingand location analyticssolutions is strong. The adoption curve from shopping centers, convention centers, airports, stadiums, and hotels has been particularly high as consumer behavior has become a key driver of business decisions and investments. Together, ALE and Aislelabs will help these businesses engage with their visitors, better understand customer behaviors and improve the customer experience.

“We have been seeking the right partner to help us address the rising demand for location based marketing and analytics solutions that complement our LAN infrastructure offering,” said Ashish Saxena, ALE Director Technical Sales & Services (TSS) for Middle East & Africa. “Aislelabs’ unique ability to assess the ROI data and close the marketing loop gives us the advantage of extending our conversations from the IT teams to the business decision makers and marketers as well. Many of our customers look for location precision and data, which is provided by our Alcatel-Lucent OmniAccess® Stellar range of products. With this partnership, we are now able to provide our customers with a single destination for their Wi-Fi infrastructure and analytics needs.”

Aislelabs focuses on eliminating complexity for location marketing by building a powerful automation platform for brick and mortar businesses of all sizes. Aislelabs allows organizations to automate various customer touchpoints and boost engagement by creating comprehensive customer journeys to help enterprises get a 360° view of the customer.

“Aislelabs is rapidly growing in the Middle East region, and we have more than doubled our team and grown our revenue year-over-year by 300 percent,” said Nilesh Bansal, CTO, Aislelabs. “We are constantly looking for partners to market and co-sell complementary solutions to our mutual customers, and the strong vertical presence of ALE aligns with Aislelabs’ target industries such as transportation, retail, hospitality and government.”


Soundcore Vortex offers rich sound and ergonomically designed headband

Enhanced audio experience with rich sound and comfortable ergonomically designed headband

Anker Innovations’ highlights Soundcore Vortex Wireless Over-Ear Headphones, with 20-Hour Playtime, Bluetooth 4.1, Hi-Fi Stereo Sound, Soft Memory-Foam Ear Cups and Built-in Microphone.

Get swept away by the music and engross yourself in rich, professionally-tuned audio with AptX high fidelity sound. Every aspect of your music is heightened with brilliant treble, smooth mid-ranges, and deep bass.


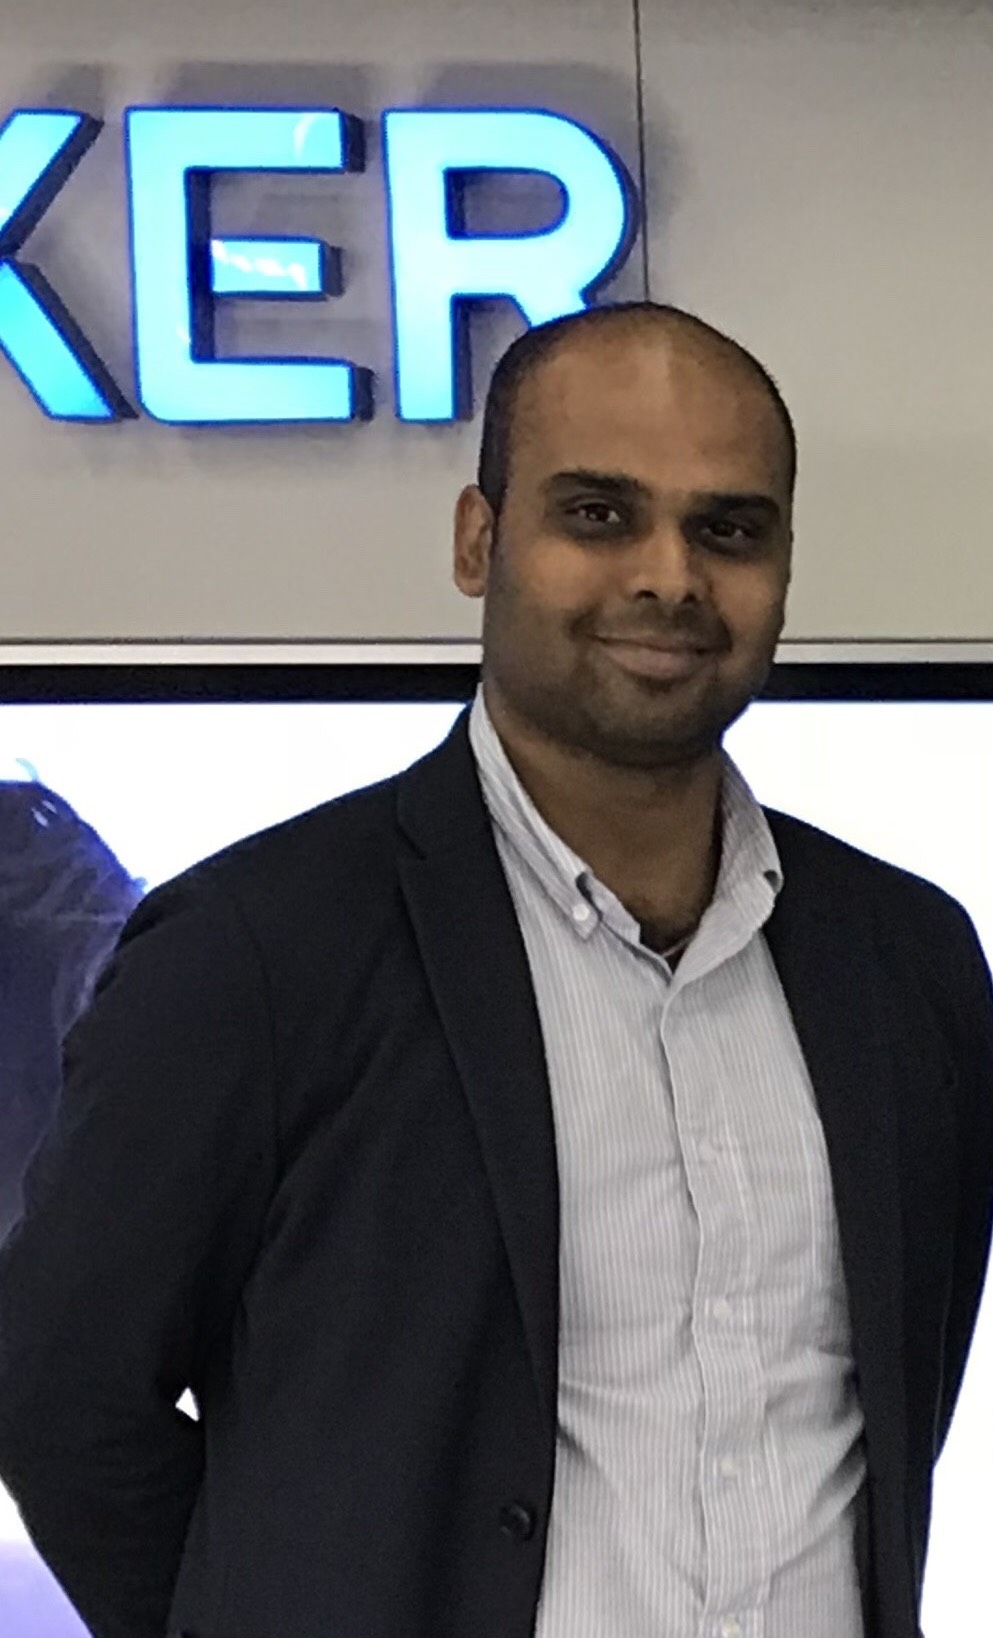
Roshan Vadlakonda, Regional Sales Head at Anker Innovations MEA .jpeg

Roshan Vadlakonda, Regional Sales Head at Anker Innovations MEA

Roshan Vadlakonda, Regional Sales Head at Anker Innovations MEA said, “We are delighted to bring in Anker’s world class innovations through our amazing audio brand Soundcore to our regional market. Soundcore has a wide range of top-notch feature packed audio products and Vortex is one of our best-selling bluetooth headphones with amazing features combined with a high-performance Li-Polymer battery with Anker’s leading power management technology for up to 20 hours of playtime in wireless mode. We are glad to bring this product to all the music lovers in our region.”


For comfort, the memory foam filled ear-cups covered in soft, synthetic Leather and ergonomically designed headband offer an exceptionally secure fit. Vortex’s built-in microphone and multi-function button allows answering calls without removing headphones or reaching for the phone.

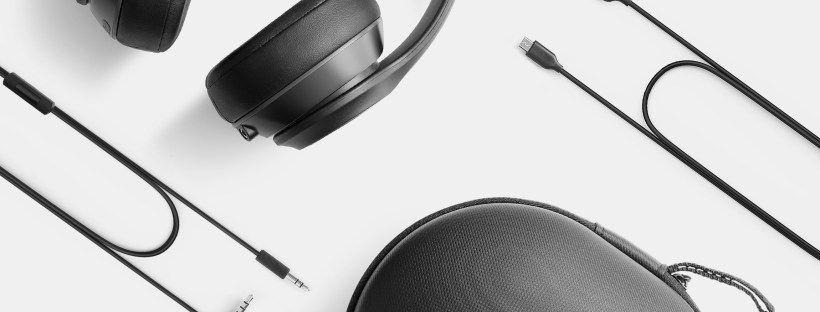
Soundcore Vortex can be folded flat and stores together with its accessories in the hard-shell travel case. Transport your headphones safely while you travel, or stay organised at home and work. Vortex is paired with a hard-shell travel care for safe storage.

Soundcore Vortex comes with a 3.5 mm aux cable, Micro USB cable, travel case and welcome guide.

Soundcore Vortex Wireless Over-Ear Headphones, offers 20-Hour Playtime and exceptional stereo Sound

Enhanced audio experience with rich sound and comfortable ergonomically designed headband

 Anker Innovations’ highlights Soundcore Vortex Wireless Over-Ear Headphones, with 20-Hour Playtime, Bluetooth 4.1, Hi-Fi Stereo Sound, Soft Memory-Foam Ear Cups and Built-in Microphone.

Get swept away by the music and engross yourself in rich, professionally-tuned audio with AptX high fidelity sound. Every aspect of your music is heightened with brilliant treble, smooth mid-ranges, and deep bass.


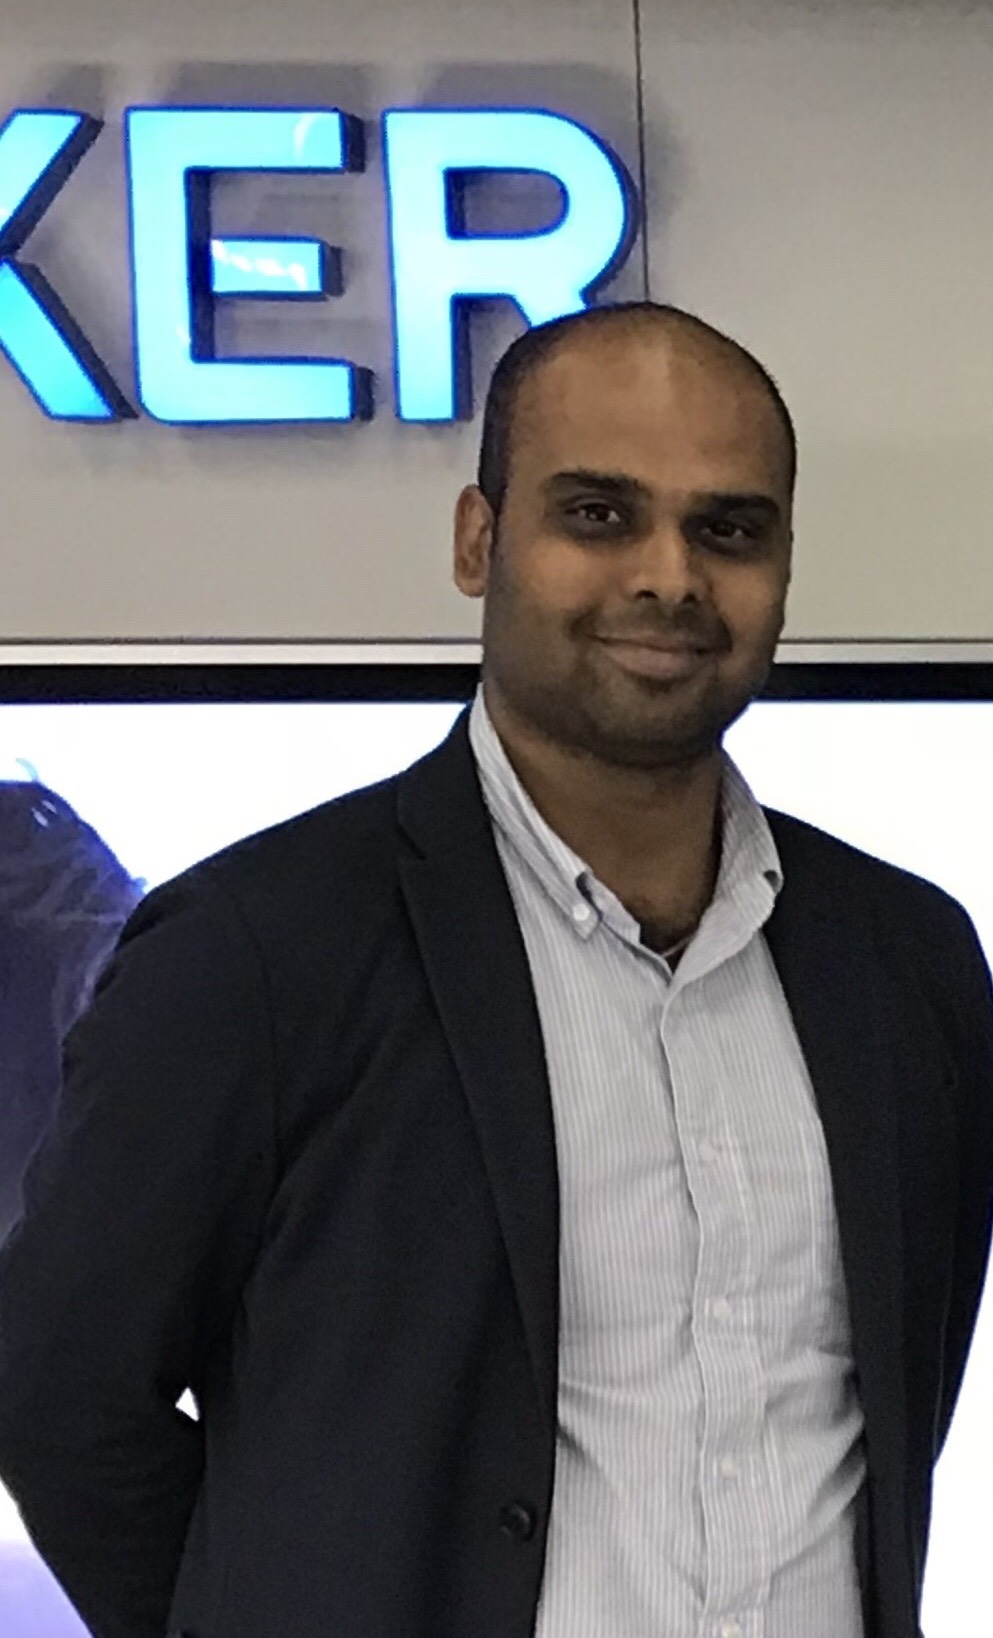
Roshan Vadlakonda, Regional Sales Head at Anker Innovations MEA .jpeg

Roshan Vadlakonda, Regional Sales Head at Anker Innovations MEA

Roshan Vadlakonda, Regional Sales Head at Anker Innovations MEA said, “We are delighted to bring in Anker’s world class innovations through our amazing audio brand Soundcore to our regional market. Soundcore has a wide range of top-notch feature packed audio products and Vortex is one of our best-selling bluetooth headphones with amazing features combined with a high-performance Li-Polymer battery with Anker’s leading power management technology for up to 20 hours of playtime in wireless mode. We are glad to bring this product to all the music lovers in our region.”


For comfort, the memory foam filled ear-cups covered in soft, synthetic Leather and ergonomically designed headband offer an exceptionally secure fit. Vortex’s built-in microphone and multi-function button allows answering calls without removing headphones or reaching for the phone.

Soundcore Vortex can be folded flat and stores together with its accessories in the hard-shell travel case. Transport your headphones safely while you travel, or stay organised at home and work. Vortex is paired with a hard-shell travel care for safe storage.

Soundcore Vortex comes with a 3.5 mm aux cable, Micro USB cable, travel case and welcome guide.

Cyber Adversaries Up the Ante on Evasion and Anti-analysis to Avoid Detection

Fortinet Threat Landscape Index Hits Highest Point to Date, Demonstrating Continued Increase In Cyberattacks

News Summary:

Fortinet® (NASDAQ: FTNT), a global leader in broad, integrated, and automated cybersecurity solutions, today announced the findings of its latest quarterly Global Threat Landscape Report.

  • The research reveals that cybercriminals continue to look for new attack opportunities throughout the digital attack surface and are leveraging evasion as well as anti-analysis techniques as they become more sophisticated in their attempts.
  • The Threat Landscape Index crossed a milestone this quarter. It is up nearly 4% from its original opening position year-over-year. The high point during that year-long timeframe is the peak and closing point of Q2 CY2019. The upsurge was driven by increased malware and exploit activity.
  • For a detailed view of the Threat Landscape Index and subindices for exploits, malware, and botnets, as well as some important takeaways for CISOs read the blog.

“The ever-widening breadth and sophistication of cyber adversaries’ attack methods is an important reminder of how they are attempting to leverage speed and connectivity to their advantage”, said Phil Quade, Chief Information Security Officer, Fortinet. “Therefore, it is important for defenders to do the same and to relentlessly prioritize these important cybersecurity fundamentals, to position organizations to better manage and mitigate cyber risks. A security fabric approach across every security element that embraces segmentation and integration, actionable threat intelligence, and automation combined with machine learning is essential to enable these fundamentals to bear fruit.”

Highlights of the report follow.

Upping the Ante on Evasion Tactics

Many modern malware tools already incorporate features for evading antivirus or other threat detection measures, but cyber adversaries are becoming more sophisticated in their obfuscation and anti-analysis practices to avoid detection.

For example, a spam campaigndemonstrates how adversaries are using and tweaking these techniques against defenders. The campaign involves the use of a phishing email with an attachment that turned out to be a weaponized Excel document with a malicious macro. The macro has attributes designed to disable security tools, execute commands arbitrarily, cause memory problems, and ensure that it only runs on Japanese systems. One property that it looks for in particular, an xlDate variable, seems to be undocumented.

Another example involves a variant of the Dridexbanking trojanwhich changes the names and hashes of files each time the victim logs in, making it difficult to spot the malware on infected host systems.

The growing use of anti-analysis and broader evasion tactics is a reminder of the need for multi-layered defenses and behavior-based threat detection.

Under the Radar Attacks Aim for the Long-haul 

The Zegostinfostealer malware, is the cornerstone of a spear phishing campaignand contains intriguing techniques. Like other infostealers, the main objective of Zegost is to gather information about the victim’s device and exfiltrate it. Yet, when compared to other infostealers, Zegost is uniquely configured to stay under the radar. For example, Zegost includes functionality designed to clear event logs. This type of cleanup is not seen in typical malware. Another interesting development in Zegost’s evasion capabilities is a command that kept the infostealer “in stasis” until after February 14, 2019, after which it began its infection routine.

The threat actors behind Zegostutilize an arsenal of exploits to ensure they establish and maintain a connection to targeted victims, making it far more of a long term threat compared to its contemporaries.

Ransomware Continues to Trend to More Targeted Attacks

The attacks on multiple cities, local governments, and education systems serve as a reminder that ransomware is not going away, but instead continues to pose a serious threat for many organizations going forward. Ransomware attacks continueto move away from mass-volume, opportunistic attacks to more targeted attacks on organizations, which are perceived as having either the ability or the incentive to pay ransoms. In some instances, cybercriminals have conducted considerable reconnaissance before deploying their ransomware on carefully selected systems to maximize opportunity.

For example, RobbinHoodransomware is designed to attack an organization’s network infrastructure and is capable of disabling Windows services that prevent data encryption and to disconnect from shared drives.

Another newer ransomware called Sodinokibi,could become another threat for organizations. Functionally, it is not very different from a majority of ransomware tools in the wild. It is troublesome because of the attack vector, which exploits a newer vulnerability that allows for arbitrary code execution and does not need any user interaction like other ransomware being delivered by phishing email.

Regardless of the vector, ransomware continues to pose a serious threat for organizations going forward, serving as a reminder of the importance of prioritizing patching and infosecurity awareness education. In addition, Remote Desktop Protocol (RDP) vulnerabilities, such as BlueKeepare a warning that remote access services can be opportunities for cybercriminals and that they can also be used as an attack vector to spread ransomware.

New Opportunities in the Digital Attack Surface

Between the home printer and critical infrastructure is a growing line of control systems for residential and small business use. These smart systems garner comparably less attention from attackers than their industrial counterparts, but that may be changing based on increased activity observed targeting these control devicessuch as environmental controls, security cameras, and safety systems. A signature related to building management solutions was found to be triggered in 1% of organizations, which may not seem like much, but it is higher than typically seen for ICS or SCADA products.

Cybercriminals are searching for new opportunities to commandeer control devices in homes and businesses. Sometimes these types of devices are not as prioritized as others or are outside the scope of traditional IT management. The security of smart residential and small business systems deserves elevated attention especially since access could have serious safety ramifications. This is especially relevant for remote work environments where secure access is important.

How to Protect Your Organization: Broad, Integrated, and Automated Security

Threat intelligence that is dynamic, proactive, and available in real-time can help identify trends showing the evolution of attack methods targeting the digital attack surface and to pinpoint cyber hygiene priorities. The value and ability to take action on threat intelligence is severely diminished if it cannot be actionable in real-time across each security device. Only a security fabricthat is broad, integrated, and automated can provide protectionfor the entire networked environment, from IoT to the edge, network core and to multi-clouds at speed and scale.

Report and Index Overview
The latest Fortinet Threat Landscape Report is a quarterly view that represents the collective intelligence of FortiGuard Labs, drawn from Fortinet’s vast array of global sensorsduring Q2 2019. Research data covers global and regional perspectives. Also included in the report is the Fortinet Threat Landscape Index (TLI), comprised of individual indices for three central and complementary aspects of that landscape which are exploits, malware, and botnets, showing prevalence and volume in a given quarter.

Getting into the fast lane with AI

By: Fadi Kanafani, Middle East Managing Director & General Manager at NetApp.

The impact of AI is being seen across industries and geographies. AI is now a key to success for organizations and is set to be a significant contributor towards global economic growth by 2030. According to a study by McKinsey Global Institute (MGI), on average, the global gross domestic product (GDP) could increase by 1.2 percentage points per year, which would correspond to a total value added of 13 trillion US dollars.

Among a number of industry segments, the automotive industry is one of the most technologically advanced and progressive industries. It’s no surprise that the industry is a frontrunner in adopting and incorporating AI into research, design, and manufacturing processes for smarter and better outcomes and products.

When you think about AI in automotive, autonomous vehicles is likely the first use case that comes to mind. While the holy grail in the industry is full self-driving, defined as level 5, most companies are already offering increasingly sophisticated adaptive driver assistance systems (ADAS) as stepping stones towards that level of autonomy.

In an industry like automotive, the number of possible AI use cases is large and essentially divided into four segments which are autonomous driving, connected vehicles, mobility as a service, and smart manufacturing. Naturally, there are overlaps between some of these segments; success in one area can yield benefits in another. For example, autonomous driving may be a key element of a mobility-as-a-service strategy. There are also many requirements that all segments have in common, including infrastructure integration, advanced data management, security, privacy, and compliance.

There are, however, challenges to achieving full self-driving. Each car deployed for R&D generates a mountain of data; 1TB per hour per car is typical. Teams can expect to accumulate hundreds of petabytes to exabytes of data as autonomous driving projects progress. This raises several critical questions such as how to create a pipeline to move data efficiently from vehicles to train a neural network or how to efficiently prepare and label data for neural network training are some of the concerns. Some questions that need to be addressed are how much storage and compute power is needed to train a neural network, to run inference on a trained neural network and if the training cluster should be on-premises or in the cloud. It is also important to determine how to correctly size the infrastructure for data pipelines and training clusters including storage needs, network bandwidth, and compute capacity.

Cars and other vehicles are quickly transforming into connected devices, and there are a number of immediate use cases for AI in connected cars such as Personal assistants / voice-activated operations, Telematics and predictive maintenance, Infotainment/recommenders.

Today, cars use cellular and WiFi connections to upload and download entertainment, navigation, and operational data. In the near future, we’ll also see cars connecting to each other, to our homes, and to infrastructure. For example, Audi has already introduced technology to connect cars to stoplight infrastructure, enabling drivers in select cities to catch a “green wave”, timing their drives to avoid red lights. That’s just one of many opportunities to use data from connected cars.

In the future, car ownership may decline in favor of various forms of ride sharing, particularly in dense urban areas. Car companies will need to become mobility service companies to address changing consumer demand. Many car companies such as Ford and home-grown Careem are already branching out, acquiring scooter- and bike-sharing companies and creating delivery services.

The machine learning and deep learning problems in mobility-as-a-service models are significantly different than those in autonomous driving: How do you predict customer demand? How do you optimize fleet efficiency and minimize customer wait times? How do you dynamically set prices in response to demand? How do you ensure passenger physical security? How do you protect customer data, prevent fraud, and balance privacy versus convenience?

From an infrastructure standpoint, these distributed problems require different strategies and may require smart algorithms on the consumer’s device (smart phone), in the vehicle, and in the cloud, plus long-term, secure data management for compliance.

The auto industry has a lot on its plate. Companies must look for ways to increase operational efficiency to free up capital for investments like those described above. Industrial Internet of Things (IIoT) and Industry 4.0 technologies are the key to streamlining business, automating and optimizing manufacturing processes, and increasing the efficiency of the supply chain.

Common manufacturing use cases include an increased use of computer vision for anomaly detection, process control for improved quality/reduced waste, predictive maintenance to maximize productivity of manufacturing equipment.

Competition in the auto industry is also fierce. Leaders look to train their own AI specialists and developers and cooperate with other companies to maintain their standing. While these measures are intended to close the current knowledge gap, it also helps achieve the overarching goals of higher product quality, better customer experience with AI, and reducing operating costs. Innovations are the key to keeping up with IT companies in the competitive field of autonomous driving.

The benefits that AI brings to the automotive industry are perceived as excessive. At the same time, there is an increasing pressure on business representatives not to miss out on the next big thing. Industry studies usually stop at a point where they become interesting: the impact on daily work routine. It would be exciting to see which AI technology the experts in the automotive industry are working on and what challenges they face.

5 Benefits of Advanced Load Balancers for the Cloud

Author: Mohammed Al-Moneer, Regional Vice President of Sales, MENA at A10 Networks

Load balancing of application traffic has been around for a long time. But, as more organisations move to the private and public cloud, it’s undergoing significant changes. Let’s look at some of the important considerations of this evolving technology.

Three major requirements underline IT operations and DevOps today: agile, efficiency and, multi-cloud operations.

  • Agile: The movement toward public cloud is arguably driven by an organisation’s desire to deliver more functionality faster. Public clouds like Microsoft Azure and Amazon Web Services (AWS) allow organisations the capacity and capability necessary to drive that agility.
  • Efficiency: Doing more with less puts a great amount of pressure on IT operations. With infrastructure as a Service (IaaS), management is divided into infrastructure management and application management. IaaS addresses availability, elasticity and efficiency of operations, and cost. Application teams then address the efficiency of application delivery.
  • Multi-Cloud Operations: Companies prefer to keep their data within their own data centres. Most adopt a multi-cloud infrastructure to balance privacy and efficiency. Less-sensitive data may be stored in public clouds while sensitive data remains in their private cloud.

Current State of Load Balancing in the Cloud

Advanced load balancing has emerged as an important element of modern operations. Load balancing has evolved given these three requirements of DevOps. Load balancing historically only handled distributing the traffic amongst servers and, in some cases, SSL offload.

Load balancers are in the middle of an organisation’s application traffic. They’re place in a critical position to see a tremendous amount of information about the flowing traffic.

Advanced load balancing provides more value and efficiency to the operations team. This is especially true with micro-services architecture and the deployment of datacentre containers or Kubernetes environments.

 5 Benefits of Advanced Load Balancers for the Cloud

The advantages of advanced load balancing can be condensed into five main categories. Let’s take a closer look at each benefit and why advanced load balancing plays an important role in promoting team agility, improving security, streamlining workflows and using new technologies.

  1. Increased Visibility, Insights and Analytics

Increased visibility, insights and analytics allow organisations to accomplish several goals, spanning from basic to cutting-edge.

  • Improve network traffic monitoring by including application traffic with traditional infrastructure monitoring. Organisations can learn what traffic is coming and how efficiently it is being served.
  • Detailed reports and health statistics, and thus better understand how their infrastructure is performing.
  • Operations teams can complete the troubleshooting process more efficiently.
  • Analytics and insights become proactive rather than reactive. A company might notice a latency issue and work to fix it before users start sending in support tickets.
  • Use the insights to perform actions automatically. Automatically adjust the infrastructure due to a change in application traffic, or block a user identified as an attacker.
  1. Integrated Security

Load balancers are placed directly into the flow of all network traffic. That placement presents an ideal opportunity to understand the behaviour and differentiate between good and bad traffic. Load balancer can automatically detect anomalies and, as a result, stop malicious traffic.

Infrastructure security is the responsibility of public cloud providers like AWS and Azure. Application-level security is still the responsibility of application owners as per Shared Security Responsibility. It is essential organisations understand the importance of full stack security and look for load balancers with integrated security.

Security products have traditionally been overly complicated and difficult to configure. Modern security products’ makes it easy for operations teams to quickly configure and use critical functions. Advanced load balancers capable of integrating with advanced security products can increase efficiency and strengthen defences.

  1. Centralised Management

Centralised management eliminates the need to log in to individual load balancers. There you can see the entire application stack within a single pane of glass. Public clouds allow the application stack to run across multiple regions. Centralised management allows application traffic to be managed across all regions within a single console. This provides both efficiency and easy manageability.

Advanced load balancers integrate with centralised management. Central management of policies is even more valuable when load balancers are deployed across multiple clouds. This power adds centralised visibility and analytics of the environment. The centralised analytics corelates data coming from various sites. This facilitates actionable insights across the entire environment.

Observations from one site, especially related to cyber security attacks, can be used for proactive actions on other sites. For example, a cyber attacker is identified at one site they can be blocked at all sites from a central console.

  1. Automation and Multi-Cloud Integration

More than 70 percent of organisations have a multi-cloud environment. Any technology they adopt today must integrate across the entire environment. This includes public clouds, private clouds, data centres, and bare-metal servers. This requirement applies to choosing a load balancer.

It’s important that load balancers have APIs for integration. Many enterprises have already implemented continuous integration/continuous delivery pipelines. Load balancers need to integrate with DevOps toolchain and infrastructure platforms.

Full integration is achieved only when API calls are possible in all directions. DevOps tools can call the load balancer API. Load balancer can call the external API in case of an alert or event.

  1. Containers and Container-Orchestration Integration

The industry is adopting containers and container orchestration systems. According to a recent survey by 451 Research, 71% of enterprises are either using or evaluating options like Kubernetes and Docker.

Applications are moving from monolithic to a microservice architecture. Deployments are migrating from traditional hardware servers with virtual machines running on the cloud, to containers running on multiple environments.

Kubernetes and Docker have been adopted by many of the industry’s top players, including Google, Amazon, Microsoft, VMware, RedHat, IBM and more. Docker and Kubernetes have as a result become de-facto standards.

Data centre criteria should include integration with container technologies. It must automatically scale containerised applications as needed while simultaneously maintaining complete visibility. This eliminates the need to manually configure policies or manage scaling.

Given the significant benefits of cloud load balancing, it’s easy to see why organisations are turning to new and advanced load balancing solutions. Load balancing is evolving to combat the evolving threat in cyber security and businesses have taken notice.